# OneLogin identity provider
> Set up single sign-on (SSO) for Cloud Management Platform (CMP) using OneLogin
---
Site [llms.txt](/llms.txt)
---
## Before you begin
- Complete [Set up SSO and SAML](/docs/cmp/configure/access-and-security/users/sso-saml/set-up/) and [Configure the identity provider](/docs/cmp/configure/access-and-security/users/sso-saml/configure-identity-provider/).
- Capture the [IdP XML metadata](/docs/cmp/configure/access-and-security/users/sso-saml/configure-identity-provider/#upload-and-download-metadata).
- Create at least one [branded portal](/docs/cmp/configure/administration/system/branded-portals/) for this SSO provider.
- Have a OneLogin administrator account that can create applications and add users.
- Have a OneLogin organization.
## Add the OneLogin SSO provider in CMP
1. Log in to CMP as an administrator.
1. Select **Admin** > **Single Sign-On (SSO)**.
1. Select **Add** > **Generic SAML Provider**.
1. Complete the [SAML settings](/docs/cmp/configure/access-and-security/users/sso-saml/set-up/#saml-settings) form.
You need the **Single Sign-On URL** and **Metadata URL / Entity ID** for the OneLogin application setup below.
## Create the OneLogin application
In OneLogin, make sure you are in the Admin menu (`https://.onelogin.com/admin`).
1. In the main navigation menu, select the **Applications** tab.
1. Select **Add App**.
1. In the search box, type "SAML Test" and search.
1. Select **SAML Test Connector (Advanced)**.
1. Enter a **Display Name** for the app and ensure **Visible in portal** is checked.
### Configure the SAML settings
Configure the SAML settings as shown below. Find the **Metadata URL / Entity ID** and **Single Sign-On URL** in CMP, on the OneLogin SSO provider's Overview page (see [Configure the identity provider](/docs/cmp/configure/access-and-security/users/sso-saml/configure-identity-provider/)).
| SAML setting field | Notes |
| --- | --- |
| Audience (EntityID) | Metadata URL / Entity ID in CMP. |
| Recipient | Single Sign-On URL. |
| ACS (Consumer) URL Validator | Single Sign-On URL. |
| ACS (Consumer) URL | Single Sign-On URL. |
| Single Logout URL | Leave blank. |
| Login URL | Single Sign-On URL. |
| SAML not valid before | 3 |
| SAML not valid on or after | 3 |
| SAML initiator | OneLogin |
| SAML nameID format | Unspecified |
| SAML issuer type | Specific |
| SAML signature element | Response |
| Encrypt assertion | Unchecked |
| SAML encryption method | TRIPLEDES-CBC |
| Send NameID Format in SLO Request | Unchecked |
| Generate AttributeValue tag for empty values | Unchecked |
| SAML sessionNotOnOrAfter | 1440 |
| Sign SLO Request | Unchecked |
| Sign SLO Response | Unchecked |
Select **Save**.
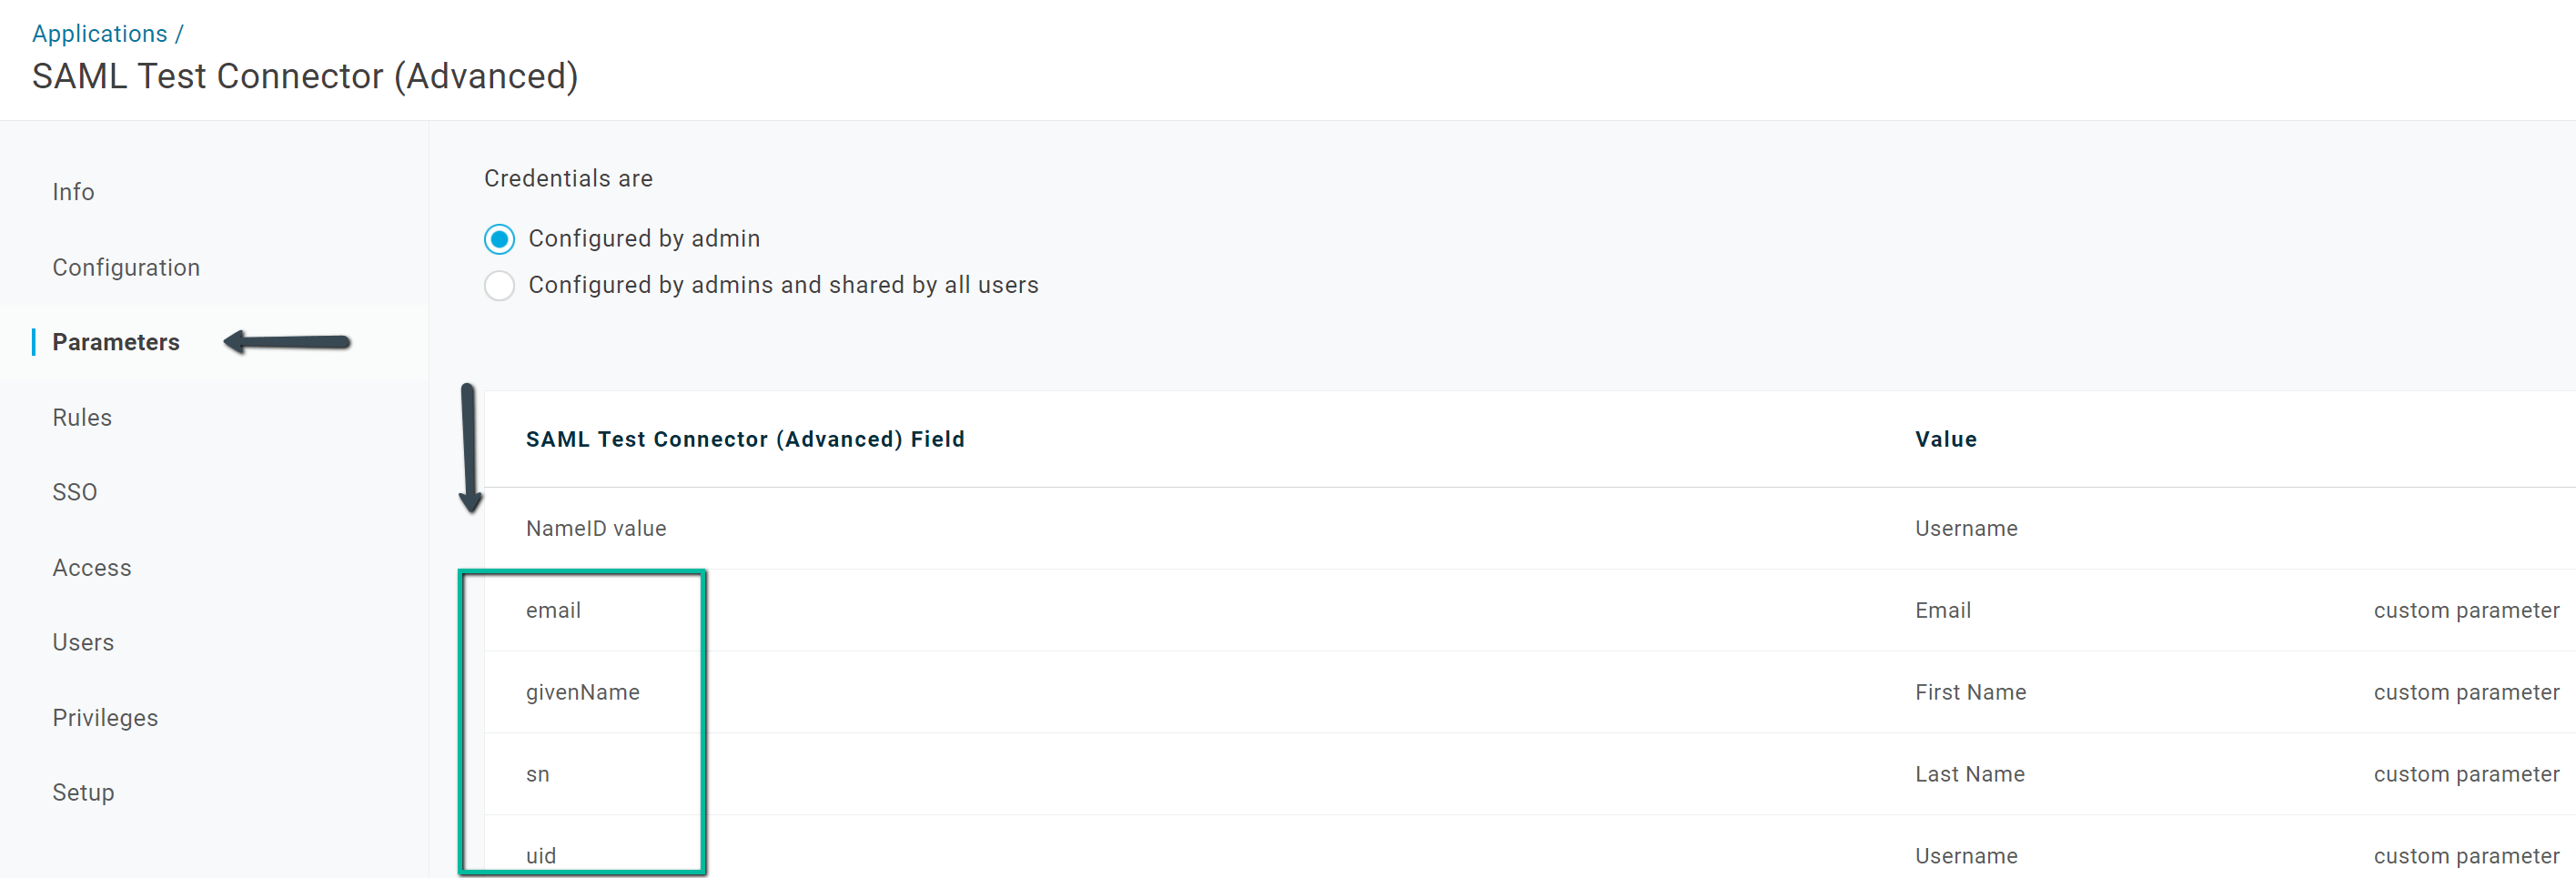
The name ID for the email, given name, surname, and user ID fields is specified as parameters within the application:
### Download the SAML metadata
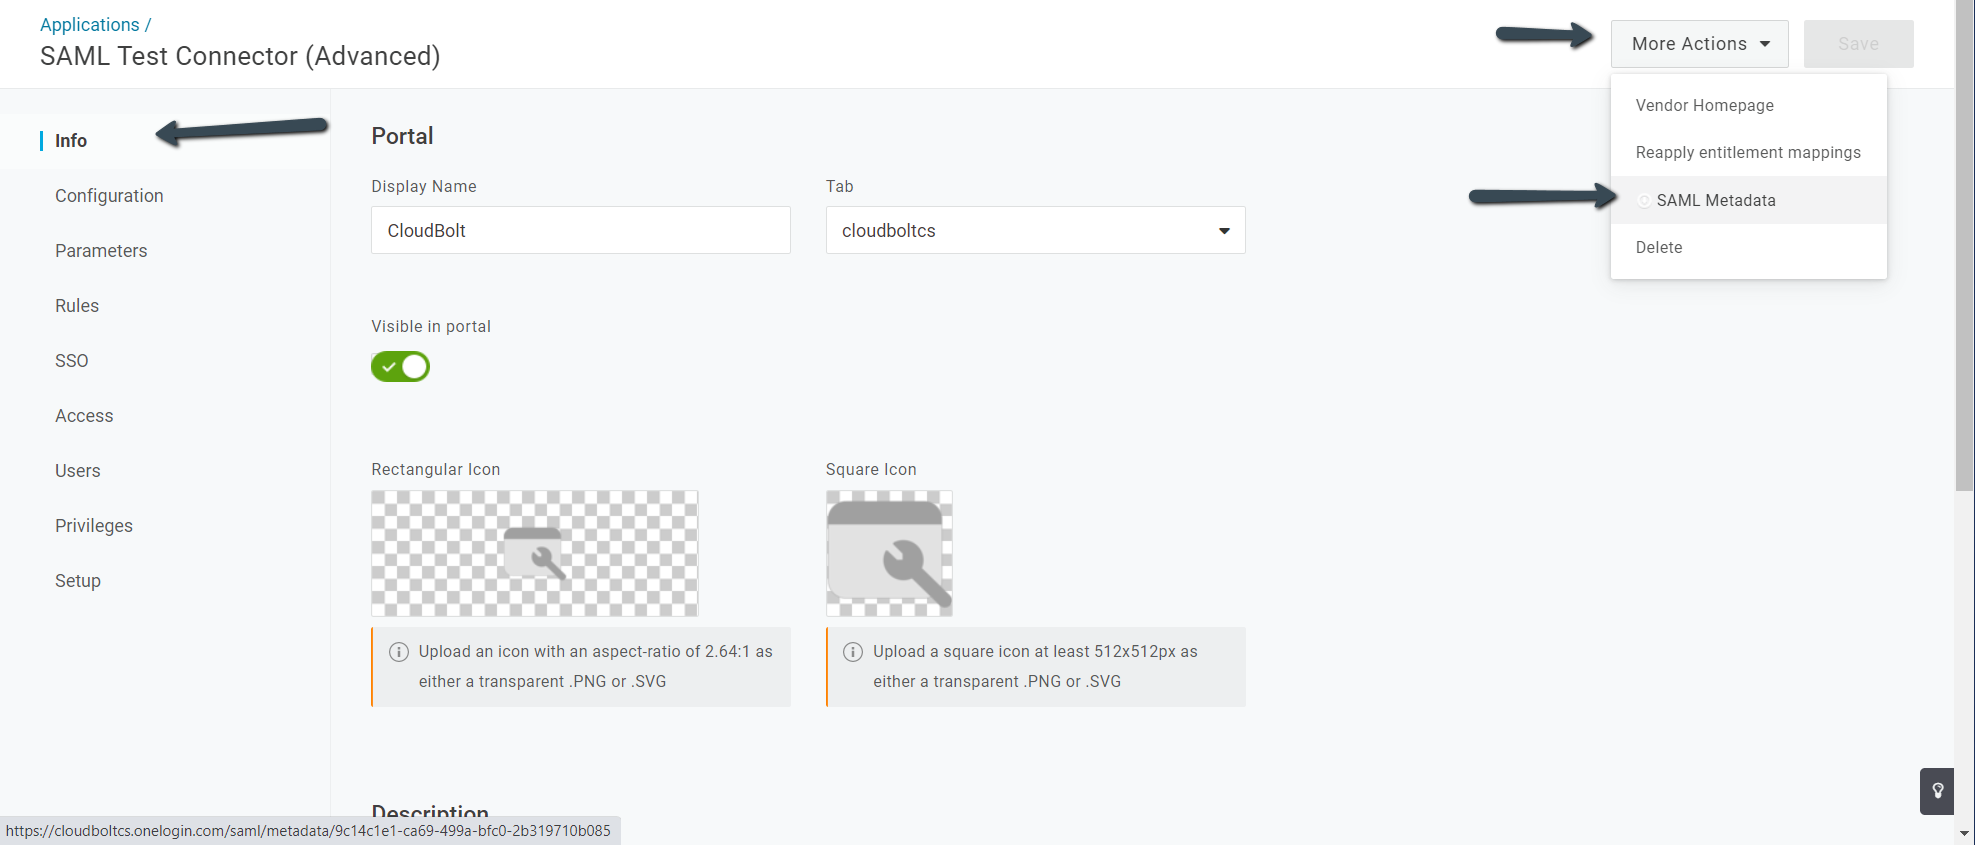
1. On the new application, select the **More Actions** dropdown in the top right.
1. Select **SAML Metadata** to trigger the file download.
### Assign user access
1. In the main navigation menu, select the **Users** tab and select the user.
1. In the left navigation pane, select **Applications**.
1. Select **[+]** in the top right.
1. Select the application and the role to assign access to the user.
1. Select **Save User**.
## Finish SSO setup in CMP
1. Log in to CMP as a Super Admin.
1. Go to **Admin** > **Single Sign-On (SSO)**.
1. Select **OneLogin**.
1. Select **Upload IdP XML**, set **Metadata source** to **Metadata File**, and choose the XML file you downloaded in [Download the SAML metadata](#download-the-saml-metadata).
1. Select the **Edit** icon.
1. If you did not choose one at setup, scroll to the **Branded Portal** dropdown and select a portal for OneLogin.
1. (Optional) Enable auto-login:
1. Select **Admin** > **Miscellaneous Settings**.
1. Set **Automatically Login to SSO** to **On**.